What Is Zero Trust? Principles, Benefits and the Security Model
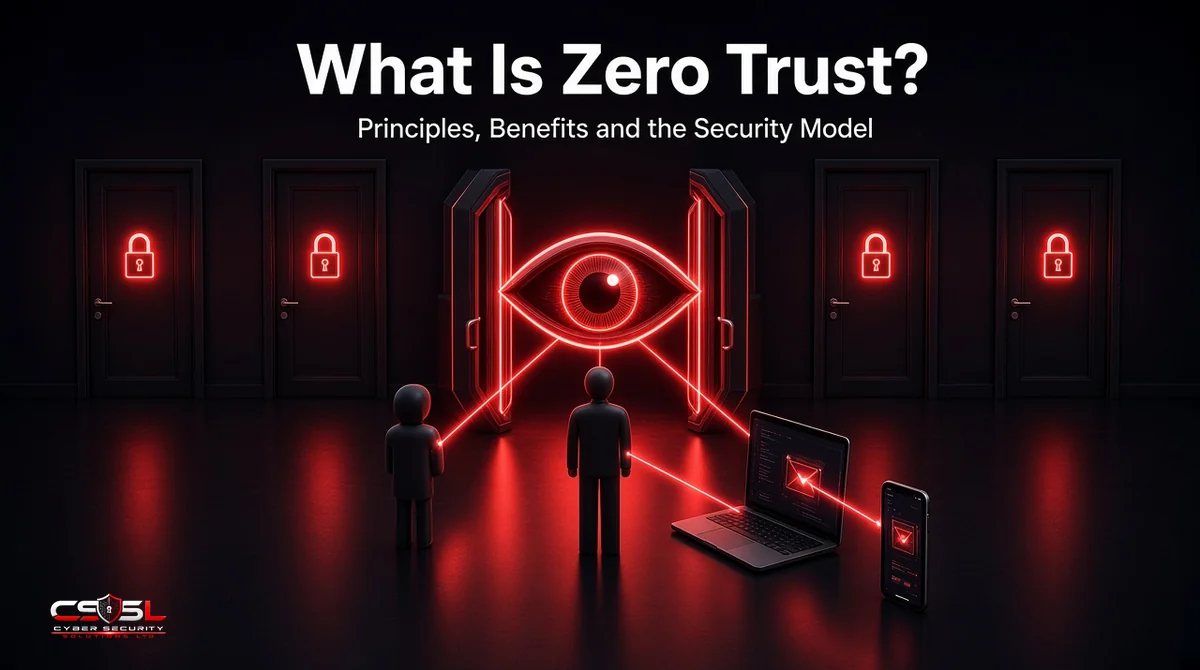
A sales manager’s password is stolen in a phishing email, and on a traditional network that one login reaches everything the VPN does. So what is zero trust? It is a security model that trusts no user, device or network by default, verifies every access request and grants only the minimum access needed.
What Is Zero Trust?
Zero trust is a security model that assumes no user, device or network location is trustworthy by default, even inside the corporate network. Every access request is checked against identity, device health and context, and users get only the access they need for that task. If an attacker gets in, the damage stays contained.
The National Institute of Standards and Technology (NIST) describes zero trust in SP 800-207 (2020) as an evolving set of cybersecurity paradigms that “move defenses from static, network-based perimeters to focus on users, assets, and resources.” The UK’s National Cyber Security Centre (NCSC) puts it more simply: zero trust is an architectural approach “where inherent trust in the network is removed.”
Zero trust is a strategy, not a product. No single tool makes an organization zero trust. It is a way of designing access that many tools help deliver.
The Problem Zero Trust Solves: Implicit Trust Inside the Perimeter
Traditional security followed a castle-and-moat model. Firewalls guarded the edge, and anything inside the network, or connected through the VPN (virtual private network), was trusted. That worked when staff, servers and data all sat in one building.
It breaks down today for three reasons:
- The edge is full of targets. Verizon’s 2026 Data Breach Investigations Report (DBIR) found that ransomware victims among small businesses were often compromised through stolen credentials (38%) or unpatched vulnerabilities in edge devices (29%).
- Once inside, attackers move freely. A flat, trusted network lets one stolen login reach file servers, backups and finance systems. This is called lateral movement.
- Work no longer happens inside the castle. Staff use cloud apps from home, contractors use their own laptops, and data lives with software as a service (SaaS) providers.
Go back to the sales manager. Under zero trust, the stolen password alone fails because multi-factor authentication (MFA) is required. Even with a hijacked session, the login reaches only the customer relationship management (CRM) app the manager needs, from a device that must pass health checks. The backups and finance server were never reachable from that account.
Where Zero Trust Came From
The ideas behind zero trust are older than the name. NIST SP 800-207 (2020) traces them to the Defense Information Systems Agency (DISA) “black core” strategy and to the Jericho Forum, which in 2004 publicized “deperimeterization.” NIST credits John Kindervag, then at Forrester, with coining the term “zero trust.”
Government adoption followed. NIST SP 800-207 set out the reference architecture in 2020. Executive Order 14028 in May 2021 started the US federal move to zero trust, and the Office of Management and Budget memo M-22-09 (January 2022) set agencies specific goals to meet by the end of fiscal year 2024. In the UK, the NCSC publishes eight zero trust architecture design principles.
Core Principles of Zero Trust
Most frameworks agree on three core principles. Microsoft’s zero trust guidance states them clearly:
- Verify explicitly. Authenticate and authorize every access request using all available signals: identity, device, location and behavior.
- Use least privilege access. Give users and workloads only the access they need, for the shortest time required.
- Assume breach. Design controls expecting that attackers may already be inside, and limit what they can reach.
NIST SP 800-207 (2020) expands these into seven tenets. In short: every data source and service is a resource; all communication is secured regardless of network location; access is granted per session; access is decided by dynamic policy; the organization monitors the security posture of every asset; authentication and authorization are dynamic and strictly enforced before access; and the organization collects data to improve its security over time.
The NCSC’s principles add practical advice for UK organizations, including “know your architecture, including users, devices, services and data” and “don’t trust any network, including your own.”
The Five Pillars of Zero Trust
The most widely used way to organize zero trust work comes from the Cybersecurity and Infrastructure Security Agency (CISA). Its Zero Trust Maturity Model Version 2.0 (April 2023) uses five pillars:
- Identity: who the user or service is, proven with strong authentication.
- Devices: whether the laptop, phone or server is known, managed and healthy.
- Networks: how traffic is segmented, encrypted and monitored.
- Applications and workloads: how apps and services are accessed and protected.
- Data: what information exists, how sensitive it is and who can use it.
Three cross-cutting capabilities run across all five: visibility and analytics, automation and orchestration, and governance.
Zero Trust Maturity: Traditional to Optimal
CISA’s model rates each pillar at one of four stages. Traditional means manual configuration and static policies. Initial means automation is starting. Advanced means automated controls wherever applicable. Optimal means fully automated, just-in-time access. Few organizations sit at one stage across every pillar, and that is expected. The model is a roadmap, not a pass or fail test.
What Is Zero Trust Architecture? How an Access Request Works
Zero trust architecture (ZTA) is the set of components that turns the principles into access decisions. NIST SP 800-207 (2020) describes three core parts:
- Policy engine (PE): makes the decision to grant, deny or revoke access, using policy and inputs such as threat intelligence and device data.
- Policy administrator (PA): carries out that decision by opening or shutting down the connection.
- Policy enforcement point (PEP): the gatekeeper between the user and the resource that enables, monitors and ends each connection.
Here is a typical request. A user opens the payroll app. The PEP passes the request to the policy engine. The engine checks the user’s identity and MFA, the laptop’s patch level and encryption, the time and location, and the sensitivity of payroll data. If everything meets policy, the administrator tells the PEP to open a session to the payroll app only. If the laptop later fails a health check, the session can be cut.
Benefits and Common Misconceptions
Done well, zero trust delivers clear benefits:
- A smaller attack surface, because applications are not exposed to everyone on the network.
- Less lateral movement, so one compromised account or device cannot reach everything.
- Safer remote and hybrid work, with the same checks at home and in the office.
- Better visibility, because every access decision is logged.
- Easier audits, since access policies are written down and enforced consistently.
Three misconceptions slow organizations down. First, zero trust does not mean distrusting employees; it means not trusting network location. Second, it is not something you buy in one purchase. Third, it is not only for large enterprises. The building blocks (MFA, device management and least privilege) are within reach of a 20-person firm.
A Zero Trust Starting Plan for Small and Mid-Sized Businesses
Most zero trust guidance is written for federal agencies or large enterprises. In most SMB environments we review, the fastest progress comes from doing five things in order, using tools many businesses already pay for.
- Start with identity. Turn on MFA for every account, starting with email, cloud apps and administrator accounts. For UK firms, Cyber Essentials (Requirements for IT Infrastructure v3.3, 2026) already says authentication to cloud services “must always use MFA.” It also requires separate accounts for administrative work.
- Know your devices. Enroll company laptops and phones in device management, and set a rule that only managed, patched and encrypted devices can reach sensitive apps.
- Map your crown jewels. List the five to ten systems that would hurt most if breached, usually finance, payroll, client files and backups, and record who needs each one.
- Cut standing access. Remove admin rights from daily accounts, remove leavers promptly and review group membership quarterly.
- Replace broad network access. Move remote users from a full-network VPN to application-level access, one app at a time, starting with contractors.
The decision rule: do not start a network redesign until steps 1 and 2 are in place. Identity and device checks deliver most of the early risk reduction, and every later step depends on them. US businesses can use the CISA maturity model to track progress by pillar. UK businesses can map the same steps to the NCSC design principles.
What the First 90 Days Can Look Like
Here is an illustrative plan for a 50-person professional services firm on Microsoft 365 or Google Workspace:
- Days 1 to 30: enforce MFA for all users and admins, create separate admin accounts, and block legacy sign-in methods that cannot use MFA.
- Days 31 to 60: enroll every company laptop and phone in device management, set minimum patch and encryption rules, and require a compliant device for email and file storage.
- Days 61 to 90: list the crown-jewel systems and their users, remove unused admin rights, and move contractors off the VPN to application-level access.
How to Tell It Is Working
Track a few simple measures each month: the share of accounts with MFA enforced, the share of devices that meet health rules, the number of standing admin accounts, and the number of users with full-network VPN access. Each number should move in one direction. If one stalls, that pillar needs attention before you add new tools.
Where regulated data is involved, such as health or payment card data, confirm how these controls fit your HIPAA, UK GDPR or PCI DSS obligations with your auditor or counsel.
Start Your Zero Trust Program With One Identity Decision This Month
If someone asks what is zero trust in practice, the honest answer is a series of small decisions that remove automatic trust, one system at a time. The best first decision is identity: pick the account type with the widest access, usually email and cloud admin accounts, and enforce MFA on it this month. Next quarter, add device health checks to the same apps. If you want help prioritizing your first steps, Cyber Security Solutions Ltd offers a free, no-obligation cyber security assessment, which you can request through our contact page.
FAQs
CISA's Zero Trust Maturity Model Version 2.0 (April 2023) lists five pillars: identity, devices, networks, applications and workloads, and data. Three cross-cutting capabilities support them: visibility and analytics, automation and orchestration, and governance. Each pillar is rated from traditional to optimal, so organizations can track progress area by area.
Zero trust is a strategy. Products such as MFA, device management, zero trust network access (ZTNA) and microsegmentation tools help deliver it, but none makes an organization zero trust on its own. Be cautious of any vendor claiming one product delivers full zero trust. Judge tools by which pillars and principles they support.
NIST credits John Kindervag with coining the term "zero trust" while he was an analyst at Forrester. The ideas came earlier, including DISA's "black core" work and the Jericho Forum's 2004 push for deperimeterization. NIST then formalized zero trust architecture in SP 800-207, published in 2020.
Zero trust is the overall security model covering identity, devices, networks, applications and data. ZTNA is one technology within it that gives users access to specific applications instead of whole networks, often replacing a VPN. You can deploy ZTNA without reaching zero trust, because devices, data and identity still need their own controls.
Implicit trust based on network location is not a zero trust principle; it is the idea zero trust replaces. Granting broad access after one login, trusting devices because they are on the office network, and treating internal traffic as safe all contradict zero trust. Its principles are explicit verification, least privilege and assuming breach.
There is no fixed timeline. US federal agencies were given roughly three years under OMB memo M-22-09, from January 2022 to the end of fiscal year 2024, and zero trust is best treated as an ongoing program. Small businesses can make meaningful progress within months by starting with MFA, device management and least-privilege access.