Network Security for Financial Institutions: Compliance and Protection Guide
Network security for financial institutions centers on isolating SWIFT-connected infrastructure into a dedicated secure zone with strict segmentation and MFA, securing branch networks containing many agentless devices like ATMs and cameras, and extending Cardholder Data Environment scoping principles across the full institutional network, not payment systems alone.
If you’re SWIFT-connected and not confident your local network environment is genuinely segmented from your corporate network, this guide gets specific about exactly what that requires.
What Does This Post Cover That Isn’t Already Addressed Elsewhere?
This brand’s separate cloud security content already covers DORA, cloud concentration risk and personal regulatory accountability in depth. This pillar’s own dedicated compliance content already covers PCI DSS Cardholder Data Environment scoping mechanics in genuine detail.
This guide’s own job is different: the physical and logical network architecture inside a financial institution specifically. That means branch networks, ATM infrastructure, and critically, the local network environment surrounding an institution’s own SWIFT connectivity.
The Bangladesh Bank Heist — the Incident That Created an Entire Compliance Regime
In February 2016, attackers stole $81 million from Bangladesh Bank by issuing fraudulent SWIFT transfer instructions, out of a considerably larger attempted theft.
Here’s the crucial nuance most competitor content gets wrong. SWIFT’s own global messaging network was never breached and performed exactly as designed. The fraud succeeded specifically because attackers compromised the bank’s own local SWIFT terminal environment, the hardware, software and credentials sitting at the bank’s own end of the connection, and used valid, if fraudulently obtained, access to submit messages the network had no basis to reject.
Attackers also modified the bank’s own local SWIFT software to suppress incoming confirmation messages, deliberately delaying detection while the transfers cleared.
This is precisely a network security lesson, not merely a compliance one. The industry’s direct response was isolating and hardening the local network environment around SWIFT connectivity specifically, developed next.
SWIFT CSP’s Own Network Segmentation Requirements, Mapped onto Controls You’ve Already Built
SWIFT’s Customer Security Programme requires a “secure zone” concept: the network segment where SWIFT messaging and communication interfaces reside must be logically or physically segmented from the general corporate network.
Named, well-documented segmentation failures show up repeatedly across audited institutions. Overly permissive firewall rules allow unnecessary traffic between the corporate network and the SWIFT secure zone. Flat network architectures skip proper VLAN segmentation entirely. Missing or misconfigured access control lists leave gaps nobody notices until an audit or an attacker finds them first.
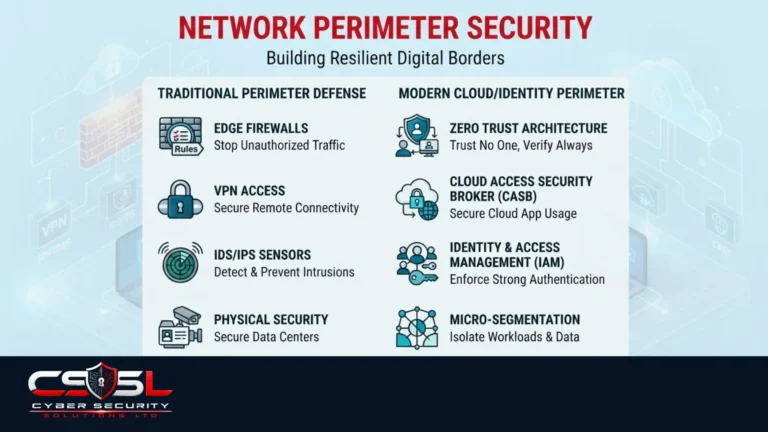
Here’s the genuinely satisfying mapping worth understanding directly. Dedicated VLANs with explicit deny-all default policies recap the same default-deny firewall principle already established generally, applied specifically here. Mandatory multi-factor authentication for every interactive SWIFT session recaps established AAA discipline directly.
The Customer Security Controls Framework, the specific mandatory control set every SWIFT user must implement, is worth naming as genuinely current. The 2026 version of the framework makes Control 2.4A, Back Office Data Flow Security, mandatory rather than advisory, specifically requiring protection for data flows between the SWIFT secure zone and downstream back-office systems. This closes the exact gap Bangladesh Bank attackers exploited a decade earlier, where security investment focused heavily on the SWIFT interface itself while implicitly trusting everything downstream. That’s a genuinely valuable, current detail showing this decade-old lesson is still actively shaping practice.
Annual attestation is a real, practical compliance mechanic worth naming. Every institution holding a SWIFT Business Identifier Code must submit an annual attestation, with most architecture types now requiring independent external assessment rather than simple self-attestation.
Common SWIFT Secure Zone Segmentation Failures and Fixes
| Failure | Why It Happens |
|---|---|
| Overly permissive firewall rules | Convenience rules between corporate network and secure zone never revisited |
| Flat architecture without VLANs | No dedicated segment separating SWIFT infrastructure from general IT |
| Missing/misconfigured ACLs | Access lists never explicitly defined or drift over time |
The Branch Network — ATMs, Cameras and the Agentless-Device Problem
A typical bank branch runs a surprisingly complex mix of connected devices: teller workstations, ATMs, security cameras, digital signage, HVAC controllers, guest WiFi access points and VoIP phones, alongside a direct connection back to core banking infrastructure.
Most connected devices are resource-constrained and cannot run traditional endpoint agents, a structural gap already well established for connected devices generally. Applied here specifically, a substantial share of branch devices, commonly estimated at roughly half to two-thirds, cannot support traditional endpoint security tooling at all.
ATMs represent a distinctive risk worth naming directly. An ATM is simultaneously a data system and a physical appliance directly accessible to the public. Older models frequently run embedded operating systems receiving updates less consistently than other systems, making a compromised ATM a realistic starting point for lateral movement into back-end banking systems.
Security cameras deserve their own mention as a specific, often-overlooked example. Camera systems typically run simpler, less well-secured operating systems than servers or ATMs, and their limited logging can mean lateral movement through a compromised camera network goes undetected longer than through better-monitored systems. A camera nobody’s watching the logs on is exactly the kind of quiet foothold an attacker wants.
A Recurring Pattern, Not a One-Off Incident
Bangladesh Bank was not an isolated event. A well-documented 2018 attack against Cosmos Bank in India combined compromised SWIFT access with fraudulent ATM network activity, enabling coordinated, simultaneous cash withdrawals across dozens of countries within a short window.
Naming this pattern matters. The same underlying lesson, local network compromise enabling fraudulent instructions the wider financial messaging system has no basis to reject, has recurred across multiple, separate, well-documented incidents rather than being a single historical anomaly worth treating as settled history.
The Honest Limit of Segmentation — When Stolen Credentials Bypass the Boundary Anyway
Here’s a genuine limitation worth stating directly. Even well-designed network segmentation can be overcome if an attacker gains control of a Domain Controller or otherwise obtains legitimate, valid credentials, since that access lets them masquerade as an authorized user with genuine permission to cross the boundary.
This reinforces rather than undermines the case for the controls already covered throughout this discussion. Segmentation limits the default pathways available to an attacker, but genuinely robust protection also requires identity discipline, continuous monitoring and incident response readiness, none of which segmentation alone replaces. A well-segmented network with a stolen admin credential is still a compromised network; the boundary just didn’t matter that particular time.
PCI DSS Network Segmentation, Recapped and Applied to the Wider Financial Network
Properly implemented segmentation reduces the scope of systems subject to full PCI DSS assessment by isolating the Cardholder Data Environment specifically, already covered in real depth elsewhere.
Here’s the genuinely useful application worth adding. A financial institution’s own network architecture typically extends well beyond payment-card handling alone. The same segmentation discipline established for CDE scoping should extend consistently across branch, ATM, core banking and SWIFT-connected zones alike, rather than being narrowly applied only to the specific systems PCI DSS itself governs.
SWIFT CSP vs PCI DSS Network Requirements
| Criteria | SWIFT CSP | PCI DSS |
|---|---|---|
| What it protects | Payment messaging infrastructure | Cardholder data environment |
| Segmentation requirement | Dedicated secure zone, deny-all default | CDE isolation from general network |
| Attestation process | Annual attestation, independent assessment for most architectures | Annual assessment, scope validated by QSA |
How Do You Secure a Financial Institution’s Network Step by Step?
- Isolate any SWIFT-connected infrastructure into its own dedicated, deny-all-by-default secure zone.
- Require multi-factor authentication for every interactive session with SWIFT-related systems specifically.
- Inventory every device type present in a typical branch, including ATMs and security cameras.
- Segment branch networks deliberately rather than treating them as a single, flat network sharing a direct connection to core banking infrastructure.
- Layer identity and monitoring controls alongside segmentation, given that segmentation alone can be bypassed by a genuinely compromised credential.
- Apply CDE scoping and segmentation methodology across your institution’s full network, not only the specific systems handling payment card data.
- Prepare for SWIFT CSP’s annual attestation cycle by testing and documenting your secure zone’s segmentation architecture on a recurring, not one-time, basis.
Conclusion
Financial institution network security comes down to one clear lesson repeated across every major incident: the wider payment network rarely fails, the local environment around it does. Segment your SWIFT infrastructure deliberately, inventory every branch device, and pair that segmentation with real identity and monitoring discipline. If you want help testing whether your own secure zone genuinely holds up, Cyber Security Solutions Ltd can walk through it with you.
FAQs
Yes. SWIFT's global messaging network was never breached in the Bangladesh Bank heist and performed exactly as designed. The fraud succeeded through compromise of the bank's own local terminal environment, not any weakness in SWIFT's network itself.
A SWIFT secure zone is the network segment where SWIFT messaging and communication interfaces reside, required by the Customer Security Programme to be logically or physically segmented from an institution's general corporate network.
Attackers compromised the bank's own local SWIFT terminal environment using valid, fraudulently obtained credentials, then submitted transfer instructions SWIFT's network had no basis to reject, while suppressing confirmation messages to delay detection.
Use dedicated VLANs with explicit deny-all default firewall policies, require multi-factor authentication for every interactive SWIFT session, and eliminate overly permissive firewall rules between the corporate network and the secure zone.
Yes. A compromised Domain Controller or stolen, legitimate credentials let an attacker masquerade as an authorized user, crossing segmentation boundaries that would otherwise block them, which is why identity and monitoring controls remain essential alongside segmentation.
The same segmentation discipline used for Cardholder Data Environment scoping should extend across branch, ATM, core banking and SWIFT-connected zones, since a financial institution's network typically extends well beyond payment-card handling alone.