Strategy and Governance Managed XDR: How Extended Detection and Response as a Service Works ByKevin Stratvert August 23, 2026
Strategy and Governance What Is a Managed SOC? Security Operations Centre as a Service Explained ByKevin Stratvert August 22, 2026
Strategy and Governance MSSP vs MSP: What Is the Difference and Which Does Your Business Need? ByKevin Stratvert August 22, 2026
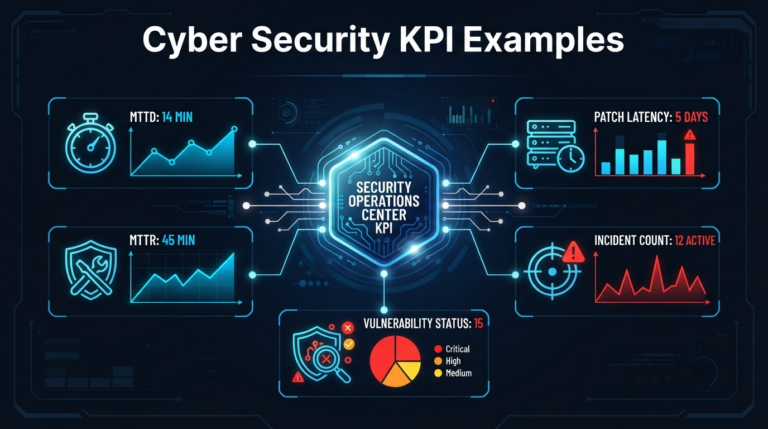
Strategy and Governance Cyber Security KPI Examples: How to Measure Your Security Programme ByKevin Stratvert August 22, 2026
Strategy and Governance What Is the CIA Triad in Cyber Security? Confidentiality, Integrity and Availability Explained ByKevin Stratvert August 18, 2026
Strategy and Governance Cyber Security ISO 27001: What It Is and How to Achieve Certification ByKevin Stratvert August 18, 2026
Strategy and Governance Information Security Policy: What It Must Include and How to Enforce It ByKevin Stratvert August 18, 2026
Strategy and Governance Cyber Security Policies and Procedures: How to Write Them Correctly ByKevin Stratvert August 17, 2026
Strategy and Governance What Is GRC in Cyber Security? Governance, Risk and Compliance Explained ByKevin Stratvert August 17, 2026
Strategy and Governance Cyber Security Governance: How to Build a Framework That Lasts ByKevin Stratvert August 17, 2026