Biometric Access Control: How It Works and Why Businesses Are Adopting It
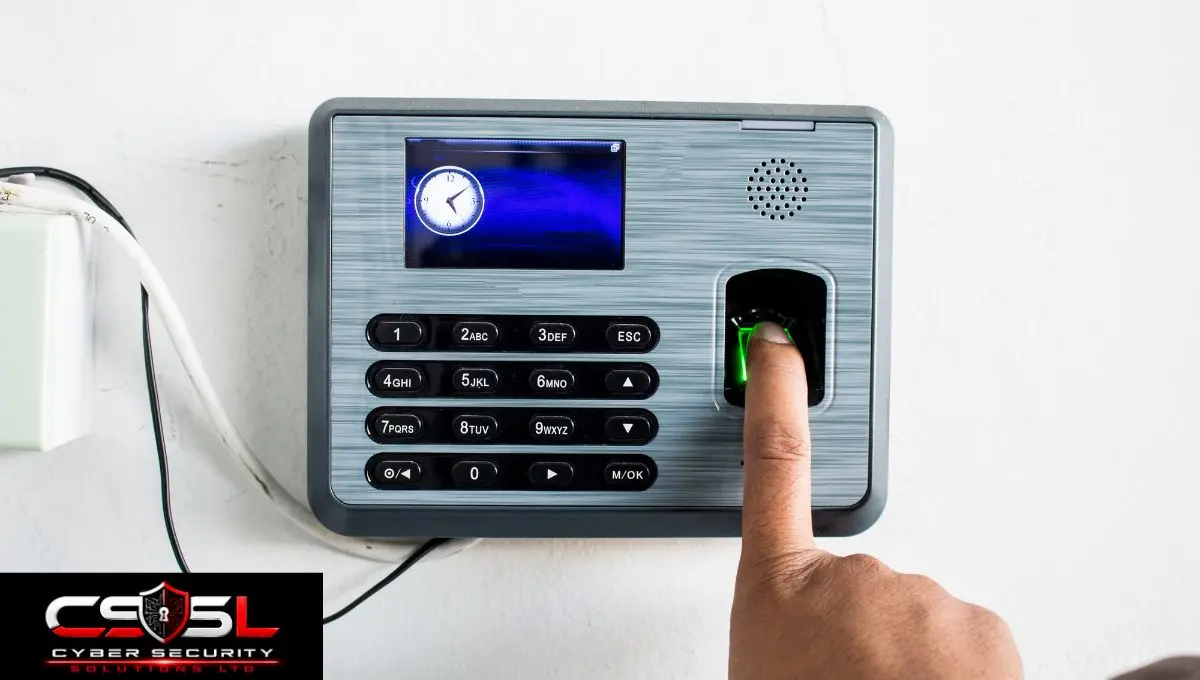
Biometric access control verifies identity using physical characteristics, fingerprints, facial recognition, iris patterns, rather than passwords or cards, and current data shows businesses are adopting it faster than the defenses against its own newest threat, deepfakes, can keep pace. If you have seen wildly inconsistent deepfake statistics circulating, understanding which figures genuinely deserve trust changes how seriously you should weigh this specific risk.
What Is Biometric Access Control and What Is Access Control in Security Generally?
Access control in security broadly means verifying identity and granting appropriate permissions before allowing entry to a physical space or digital system. Biometric access control specifically uses unique physical or behavioral characteristics, fingerprints, facial geometry, iris patterns, to perform that verification, rather than something a person knows or carries.
This distinction matters directly because biometric characteristics are considerably harder to steal or share than a password or access card, though as the next section develops directly, they are not immune to sophisticated attack, specifically through deepfake technology now able to convincingly synthesize the exact characteristics biometric systems are designed to recognize.
How Real Is the Deepfake Threat, and Which Statistics Can You Trust?
Here is the genuinely authoritative, current figure worth anchoring to directly. Entrust’s 2026 Identity Fraud Report, published November 2025 and drawing on over one billion identity verifications across 195 countries, found deepfakes now account for one in five biometric fraud attempts globally, with deepfaked selfie attempts rising 58 percent and injection attacks, feeding fabricated video directly into verification systems, rising 40 percent year over year.
Here is the honest caveat worth stating directly, since it is precisely why deepfake statistics circulating online vary so dramatically. Most attack-surface data in this space comes from vendors who sell detection and verification products, a genuine conflict of interest rarely disclosed on the statistics pages citing these figures. Different reports also measure genuinely different things entirely, one report’s “1 in 5 biometric fraud attempts” figure describes a proportion of a specific fraud category, while other reports cite year-over-year growth percentages in the thousands, describing an entirely different metric measured against a different, often much smaller starting baseline. Citing these interchangeably as if directly comparable is genuinely misleading. The Entrust figure specifically deserves weight because it draws on genuinely enormous verification volume across many industries and countries, though even this figure should be understood as one company’s own platform data, not an independent, industry-wide census. Treat any deepfake statistic without a clearly disclosed source and methodology with genuine skepticism, and prioritize figures from reports transparent about their own data source and potential commercial interest.
Humans Are Barely Better Than Chance at Spotting Deepfakes
Here is precisely what rigorous research shows, distinguished carefully from more dramatic but less rigorous vendor claims circulating alongside it. A 2024 peer-reviewed meta-analysis aggregating 56 separate studies found average human accuracy at identifying deepfakes sits at 55.54 percent, with a confidence interval crossing 50 percent, meaning humans perform only marginally better than random chance at this specific task on average.
This is a genuinely different, more defensible claim than a separate, frequently cited vendor statistic from iProov’s 2,000-person test, which found only 0.1 percent of participants correctly identified every single fake shown to them, while 60 percent still felt confident in their own ability to detect deepfakes accurately. These are not contradictory findings, they measure genuinely different things. The peer-reviewed meta-analysis measures average accuracy across many individual judgments. The vendor study measures the considerably harder standard of catching every single fake perfectly across an entire test. Both point toward the same underlying, genuine conclusion worth taking seriously: human judgment alone is not a reliable defense against deepfake-based biometric spoofing, regardless of which specific figure you find most persuasive, meaning technical detection layers, not human vigilance, need to carry the actual defensive weight here.
Liveness Detection and Zero-Knowledge Verification: The Current Defensive Layer
Liveness detection specifically confirms a biometric input comes from a genuinely present, living person rather than a photo, video or synthetic reproduction, often analyzing micro-movements, subtle facial shifts, blinking patterns, texture changes under varying light, that current deepfake generation still struggles to replicate convincingly in real time.
Zero-knowledge biometric verification adds a complementary, genuinely distinct protection specifically around data handling, cryptographically confirming a biometric match without ever storing or exposing the raw biometric template itself. This matters directly because a stolen password can be changed, while a stolen fingerprint template genuinely cannot, making the protection of the underlying biometric data itself, not just the verification moment, a meaningful part of a complete defensive approach.
The Real Weak Point Often Isn’t the Biometric System Itself
Here is a genuinely important point worth stating directly, since it redirects attention away from where most defensive spending currently concentrates. Sophisticated biometric spoofing, deepfakes convincing enough to defeat liveness detection, remains genuinely difficult and resource-intensive for an attacker to execute reliably at scale.
The more common, practical weak point sits instead in the surrounding process, weak fallback authentication methods offered when biometric verification fails, poorly secured enrollment processes where an attacker registers a fraudulent biometric in the first place, or administrative override capabilities that bypass biometric verification entirely for support purposes. An organization investing heavily in sophisticated liveness detection while leaving a genuinely weak, easily-bypassed fallback authentication path active has not meaningfully closed its actual exposure, since attackers consistently target the path of least resistance rather than attempting to defeat the strongest control directly. This is precisely why a genuinely complete biometric access control strategy has to examine the entire process surrounding the biometric check itself, enrollment integrity, fallback authentication strength, administrative override controls, not simply the sophistication of the biometric verification technology alone.
RBAC vs ABAC: Predictability vs Precision
| Criteria | RBAC | ABAC |
| Basis | Predefined roles | Multiple dynamic attributes |
| Predictability | High, easy to audit | Lower, more complex |
| Precision | Coarser | Genuinely granular |
RBAC, Role-Based Access Control, assigns permissions through predefined roles, a user belongs to a role, and that role determines what they can access. This offers genuine predictability and straightforward auditing, since confirming what a specific role can access is simple and consistent.
ABAC, Attribute-Based Access Control, evaluates multiple attributes dynamically instead, user identity, resource sensitivity, time of day, location, combining them through policy logic, often implemented through tools like Open Policy Agent, to make considerably more precise, context-aware access decisions than a static role alone can provide. The genuine trade-off worth weighing honestly: RBAC’s predictability makes it easier to understand and audit, while ABAC’s precision handles genuinely complex, context-dependent access scenarios RBAC alone was never designed to express.
When Does RBAC Start to Break Down?
RBAC genuinely breaks down through role explosion specifically, a pattern where an organization’s access needs grow increasingly granular over time, requiring more and more specifically defined roles to capture legitimate distinctions RBAC’s own binary role membership model cannot express more efficiently.
An organization needing to grant access based on genuinely dynamic factors, a contractor’s access expiring on a specific date, a document’s access depending on its current classification level, a location-dependent restriction, finds RBAC’s static role assignment increasingly inadequate, since expressing these dynamic conditions through role proliferation alone eventually produces hundreds or thousands of narrowly-scoped roles that become genuinely difficult to manage, audit or understand collectively.
A Real Worked Example: ABAC in a Healthcare Access Scenario
Picture a hospital where a nurse needs access to patient records specifically for patients currently under their direct care, during their scheduled shift, from an approved hospital device, but should not access records for other patients or access any patient record outside their shift hours at all.
RBAC alone struggles here directly, since a single “nurse” role would need to somehow express patient assignment, shift timing and device restriction simultaneously, typically requiring an unmanageable proliferation of increasingly specific sub-roles to capture these combined conditions. ABAC handles this scenario naturally instead, evaluating the nurse’s current patient assignment, the current time against their scheduled shift, and the device’s approval status together as a single, dynamic policy decision made at the moment of each individual access request, precisely the kind of context-dependent precision this healthcare scenario genuinely requires and RBAC alone cannot efficiently provide.
What Does UK GDPR Say About Biometric Data Specifically?
UK GDPR classifies biometric data used for the purpose of uniquely identifying a natural person as special category data under Article 9, carrying genuinely stricter processing requirements than ordinary personal data, including explicit consent or another specific legal basis before collection and processing.
This means implementing biometric access control genuinely requires deliberate, documented legal basis and heightened security measures around the biometric data itself, not simply treating it as another data point collected incidentally alongside standard access logging. Cyber Security Solutions Ltd helps organizations navigate exactly this specific compliance requirement directly, since biometric data’s special category status under UK GDPR carries genuine legal weight many organizations underestimate when first considering biometric access control adoption.
Conclusion
Biometric access control genuinely strengthens identity verification, but only when paired with honest awareness of current deepfake capability and the access control model, RBAC or ABAC, that actually fits how granular your organization’s real access needs have become. Start by confirming your fallback authentication paths are as strong as your primary biometric check. To build a properly layered biometric access control strategy, visit cybersecuritysolutionsltd.com for expert support from Cyber Security Solutions Ltd.
FAQs
Access control that verifies identity using physical characteristics, fingerprints, facial recognition, iris patterns, rather than passwords or cards, offering stronger protection against theft or sharing but requiring specific defenses against deepfake-based spoofing attempts.
Genuinely significant. Entrust’s 2026 Identity Fraud Report found deepfakes account for one in five biometric fraud attempts globally, with deepfaked selfies rising 58% and injection attacks rising 40% year over year, based on over one billion identity verifications.
No. A 2024 peer-reviewed meta-analysis of 56 studies found average human accuracy at just 55.54%, barely above chance. This makes technical detection layers, not human judgment alone, essential for genuine defense against deepfake-based spoofing.
RBAC assigns permissions through predefined roles, offering predictability and simple auditing. ABAC evaluates multiple dynamic attributes, like time, location and resource sensitivity, together, offering genuinely more precise, context-aware access decisions RBAC alone cannot express.
When access needs become genuinely granular and dynamic, requiring role explosion, an unmanageable proliferation of narrowly-scoped roles, to capture distinctions RBAC’s static role model cannot express more efficiently, like time-based or context-dependent access conditions.
Yes. Biometric data used to uniquely identify someone is classified as special category data under Article 9, requiring explicit consent or another specific legal basis and heightened security measures beyond standard personal data processing requirements.